Know the estate.
Bring observations from supported sources into a common view, making coverage and unknowns explicit.
See what is running. Establish who owns it. Turn policy into action, with evidence of what actually took effect.
AI activity is growing faster than enterprises can establish ownership, policy coverage and control.
A shared operating picture, connecting observed activity to business context and accountable action.
Useful findings, verified outcomes and a repeatable reason for customers to return.
Product walkthrough · 4 min 27 sec · Narrated · No CC
From policy to action. Follow discovery, a governance-document upload, scoped approvals and a finance-agent boundary review.
Reconstructed demonstration · Illustrative data. Declared authority is not proof of enforcement; the finance example shows one sample blocked write.
An enterprise may have an AI policy without a reliable way to see where it is followed, who is accountable or which controls are working.
Canopy’s thesis is that visibility becomes more valuable when connected to ownership, business context and supported controls. The opportunity is an ongoing governance workflow, rather than another isolated inventory.
Bring observations from supported sources into a common view, making coverage and unknowns explicit.
Connect findings to policy and business ownership. Prepare scoped responses and route consequential decisions.
Keep recommendations, approvals, application results and verified outcomes distinct.
Investment thesis and product direction. Repeatable deployment, customer value and commercial conversion require evidence.
Start with a customer’s policy and a relevant source of AI activity. Show a gap the customer recognises, prepare a practical response and check what an approved control actually changes.
Upload the customer’s governance document into Ask Canopy. Clarify its requirements, trace proposed boundaries to the source and review the affected scope. Authorised people approve changes; application results and verification evidence remain separate, including failures and coverage gaps.
A customer permits approved AI tools for its development team. On a covered device, Canopy surfaces another tool and links the activity to its source and business context.
Audit mode: activity is observed; nothing has been blocked.
Illustrative workflow, not a live enforcement demo. Validate policy interpretation, supported control mapping and end-to-end verification for each pilot; coverage depends on the source, permissions and deployment scope.
A declared boundary says what an agent may do. Approval records a decision. Application records a change. Verification establishes what was tested, where and with what result. Canopy keeps that chain visible, including what has not been verified.
Discover the estate. Interpret policy. Prepare scoped changes. Route decisions. Verify outcomes.
People review consequential decisions and the effects on their business.Onboarding is designed around first value: connect a relevant application or device group, see findings as they arrive and understand what to do next.
The useful result is a finding in its business context. A small estate can still reveal an important ownership gap or a question that needs attention.
Neither has an owner recorded in the connected source.
These records need review. Missing source information does not establish that nobody is responsible.
Source: selected application · Other sources not assessedConnecting, waiting, access denied, partial results and a successful empty result are distinct states.
Inspect the record, confirm what it represents and review responsibility with the relevant business owner.
Add sources, review meaningful boundaries and return to unfinished work without losing context.
This visual sequence interprets the onboarding rehearsal: first-source discovery, business context and a guided next action. Real source connections, shared tasks, accepted ownership and verified protection still require backend integration and staging acceptance. An assigned owner is not necessarily an accepted owner; a configured control does not establish enforcement.
What happened. Why it matters. What you should do.
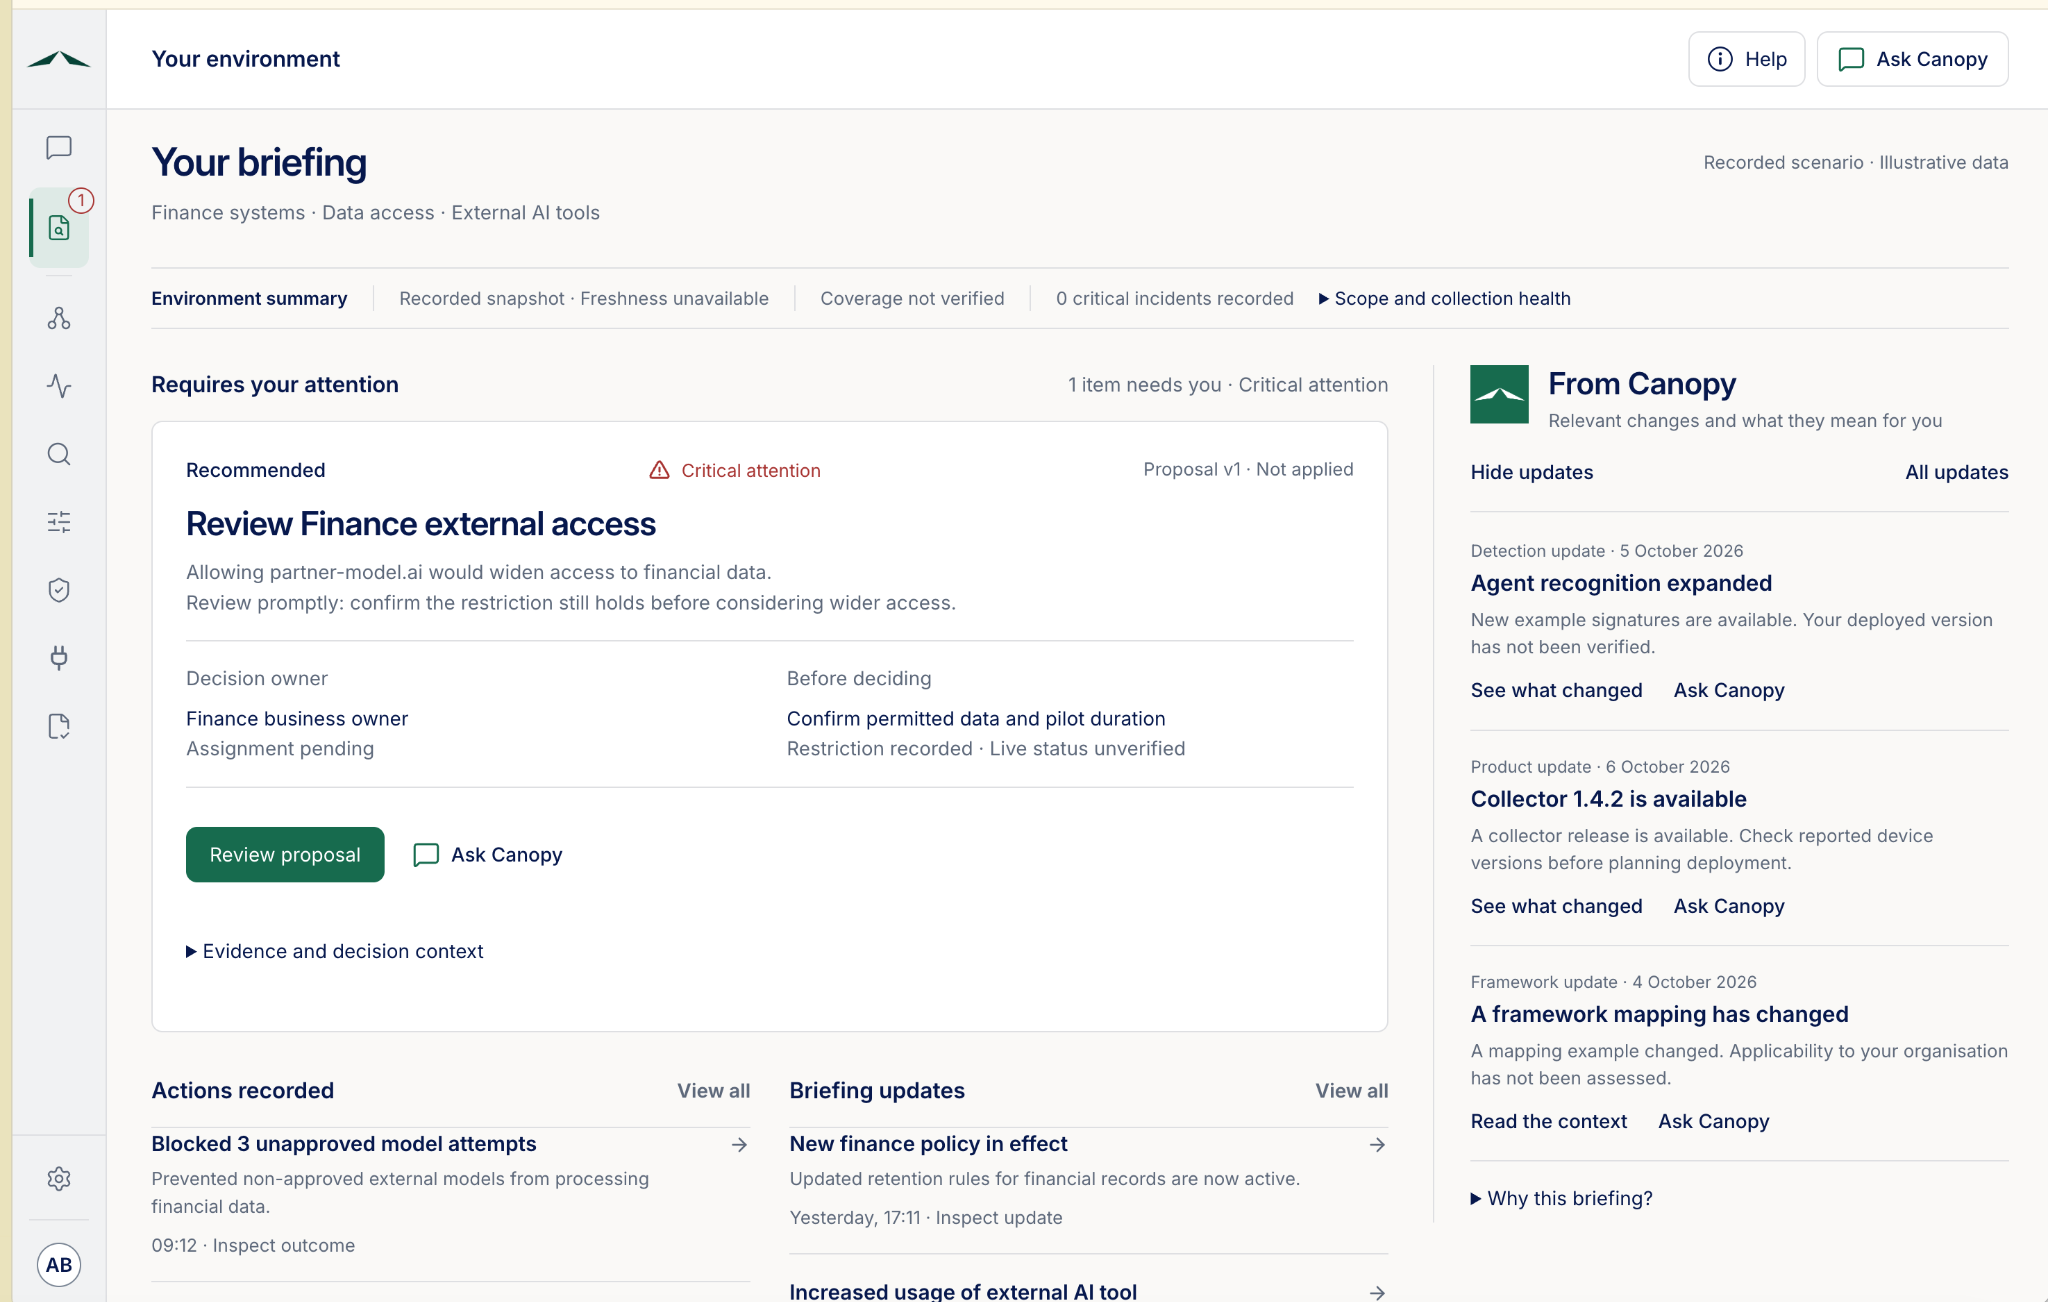
Briefing is the operational summary: what needs attention, what has been handled and what remains uncertain. Canopy is designed to act within supported controls and delegated authority, then bring consequential decisions to the right person. An alert, an approval and a resolved incident are different states.
Ask, investigate and prepare actions using the context available to your role.
A prioritised account of the environment, decisions, updates and unfinished setup.
Agents and systems, activity, governance, controls, integrations and evidence provide the detail behind each explanation.
Ask Canopy is the conversational operating surface across the platform. Ask a question in plain English, bring in a policy, inspect a finding or prepare a response in the context of your role and access. Answers link back to the underlying records. Consequential actions follow the customer’s permissions and approval requirements.
A focused evaluation should establish a recognised governance problem, a useful response and whether customers will pay to maintain the oversight. This page makes no claim of customer commitments, revenue or measured pilot outcomes.
Confirm the sponsor, relevant policy, technical access and a manageable deployment boundary.
Start in audit mode. Record coverage, findings and what remains unknown.
Test an authorised, supported control and record its outcome, business impact and delivery effort.
Review recurring usefulness, willingness to pay and the cost of delivering and supporting the workflow.
The proposed model is a platform subscription for ongoing visibility, governance workflows, exception review and evidence across an agreed scope.
Pricing, delivery economics, security readiness and the route to market should be reviewed with current evidence. No forecast, certification, partner arrangement or investment terms are asserted here.
Canopy brings together endpoint observations, supported browser activity and connected services. Its context layer relates those signals to identity, ownership, business purpose and policy.
Supported controls and their outcomes feed back into the operating record, connecting what was seen, what was decided and what took effect.
Identity · ownership · relationships
Policy context · analysis
Review consequential decisions
Apply within scope · verify outcomes
Control outcomes return to the evidence record. Recommendation, approval, application and verification remain distinct.
A process can act locally without a network request. The architectural approach includes relevant execution and file activity. Collection support, permissions and behaviour must be validated for each operating system.
Attribution across processes and runs, durable identity, ownership and policy scope make observations useful. Reliable collection, tolerable overhead and trustworthy control outcomes are substantial engineering tasks.
The intended compounding value is an established operating record: relationships, decisions, review routines and evidence. Reliable coverage and repeatable deployment must earn customer retention.
Canopy is intended to connect the wider AI estate and its operating context. Native platform controls remain important. The pilot should establish where Canopy adds useful visibility or workflow across the selected environment.
Review collection scope, permissions, data flows, retention, tenant isolation, performance and failure behaviour with the customer’s technical team. Confirm the available deployment model and integrations for that customer.
| Surface | Approach | Scope to establish |
|---|---|---|
| Managed endpoints | Process and resource observations; configurable local controls. | OS support, permissions, attribution, overhead and failure behaviour. |
| Browser AI use | Supported browser collection. | Installed extension and browser coverage; provider-side execution remains outside this view. |
| SaaS / embedded agents | Context exposed through each integration. | Provider APIs determine available identity, activity and control depth. |
| Intelligence & governance | Analysis, explanation and draft-response assistance. | Policy conversion, delegated actions and verification require capability-specific validation. |
Systems describe how agents are organised around work. Activity shows observed interactions. Locations add deployment context; runtime location alone does not establish data residency.
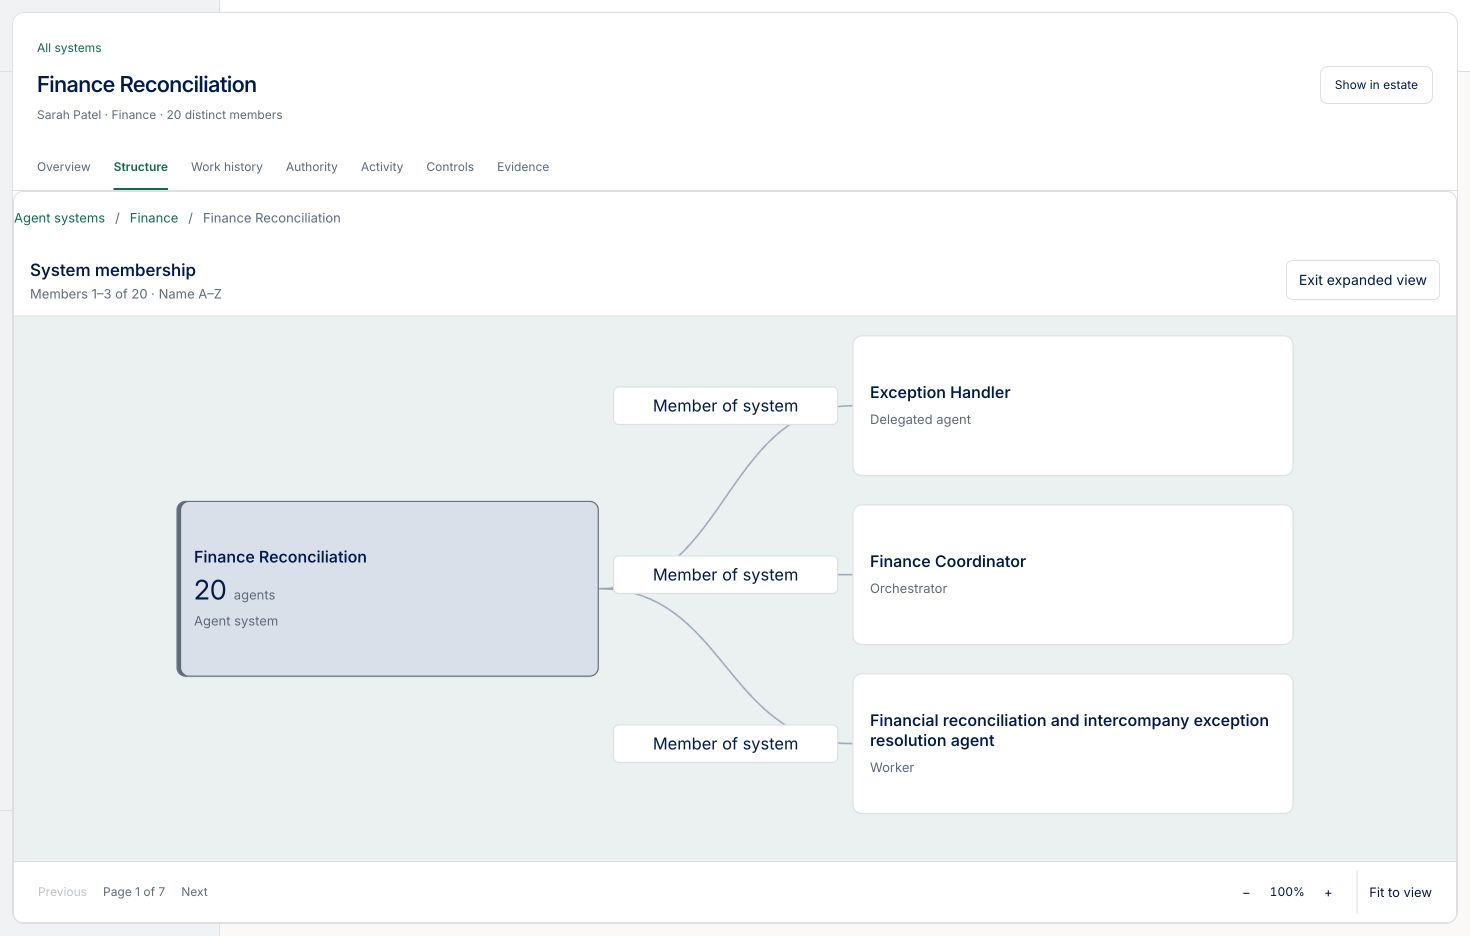
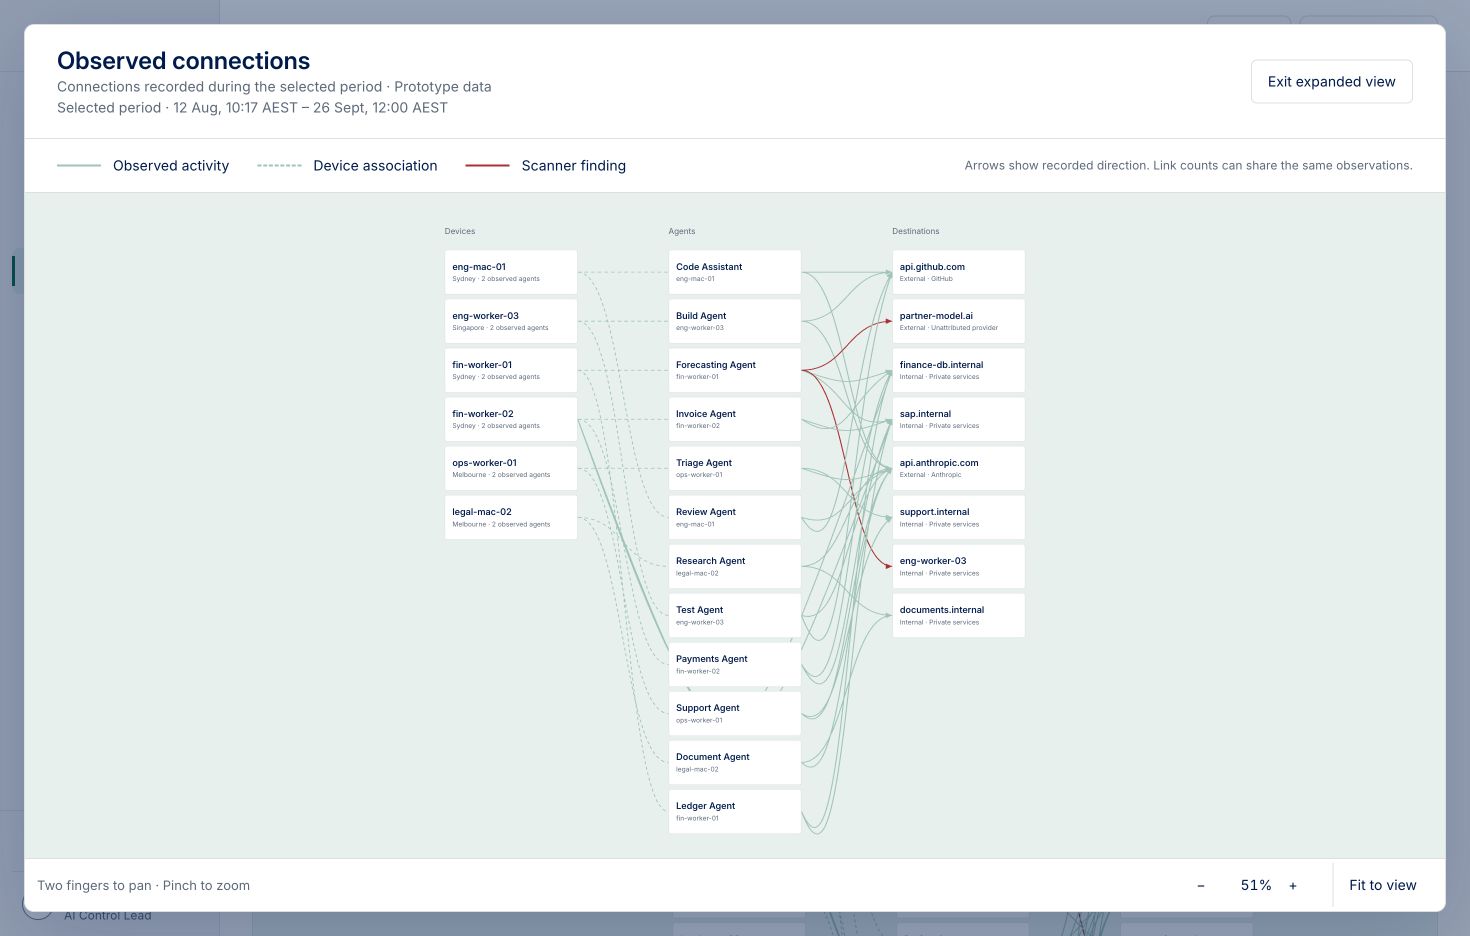
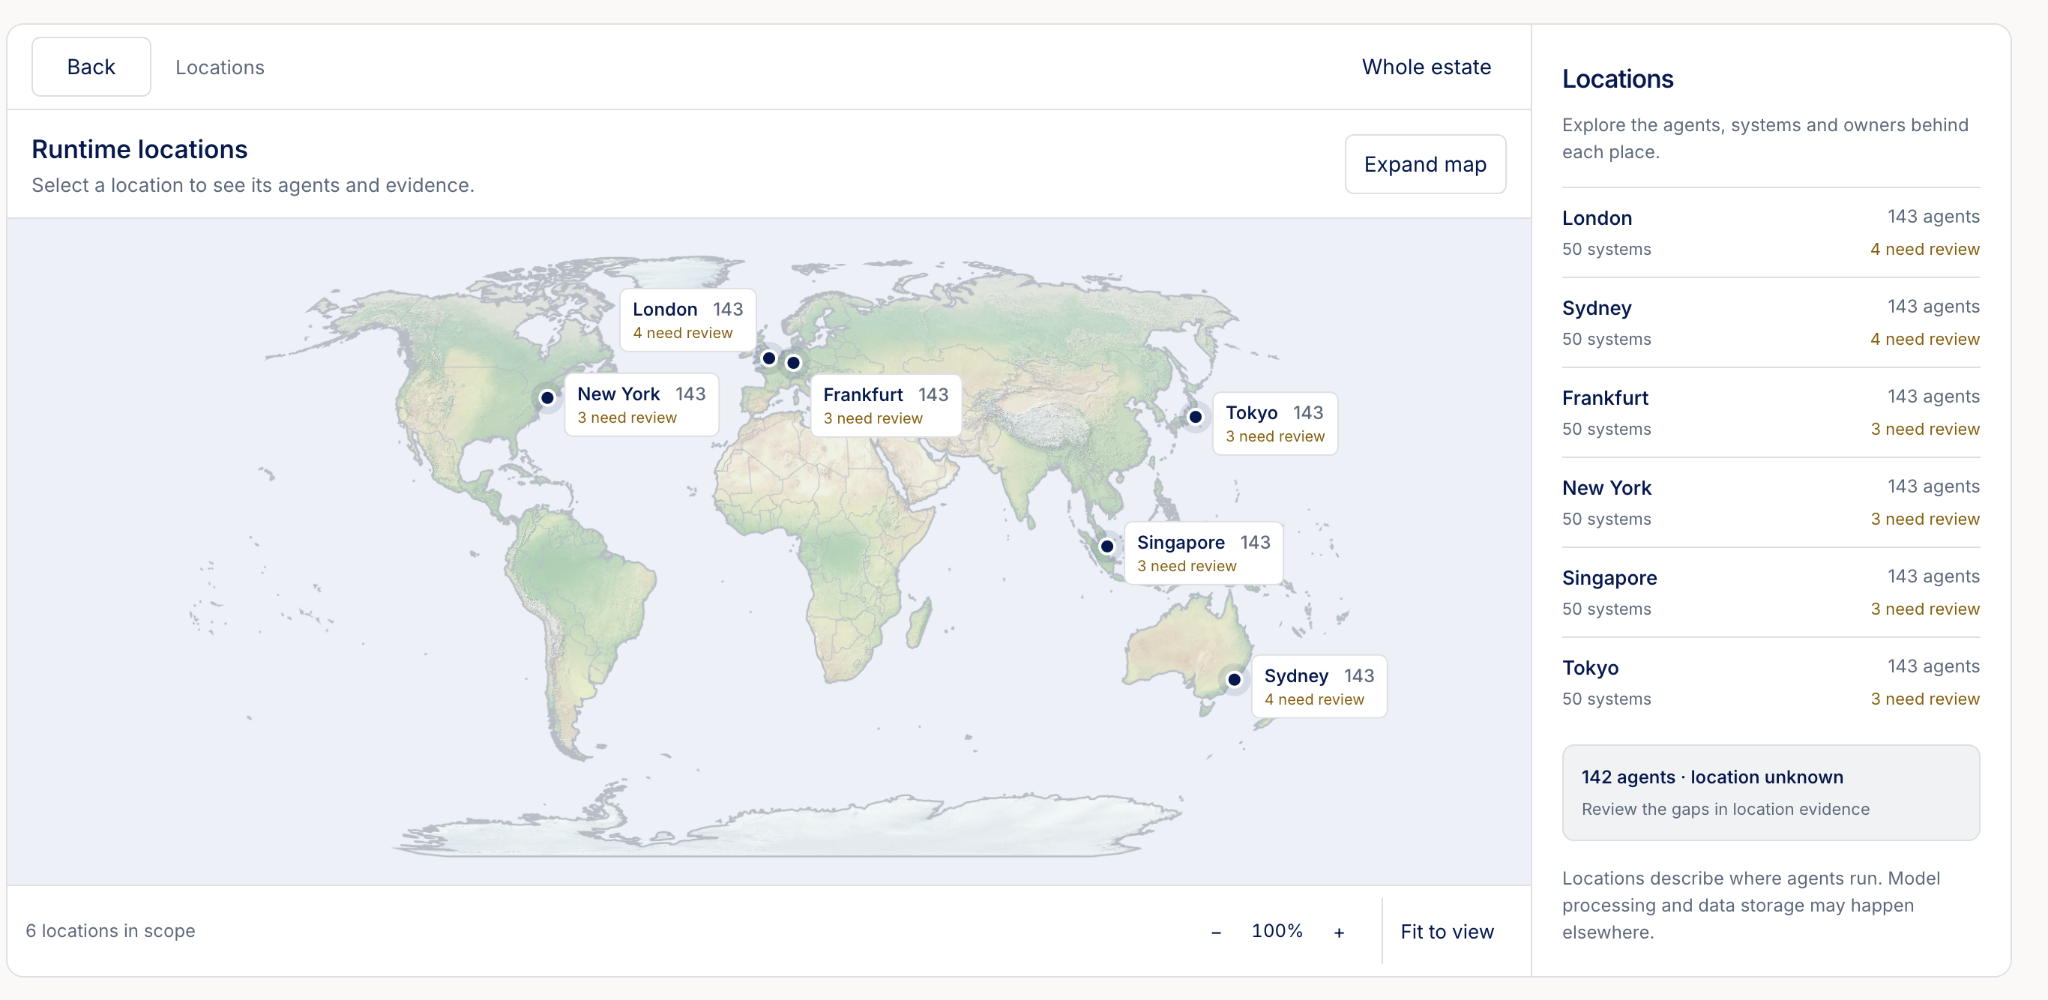
Security, risk and business owners work from common context. Actions follow assigned permissions, scope and approval requirements.
Illustrative profiles
CISO
Investigate activity, review exposure and approve security boundaries within delegated authority.
Cannot override reserved approvals or another owner’s decision rights.
Head of Finance
Review finance findings, confirm business intent and approve finance-owned decisions.
Cannot change organisation-wide security boundaries or governance rules by virtue of this role.
Head of Governance & Risk
Review policy coverage, identify gaps and prepare assurance evidence for management.
Cannot apply runtime controls unless separately authorised.
The team brings together company building, enterprise security, application security and software engineering. That experience informs the controls underneath Canopy and the operating experience above them.
Technology strategy, commercial leadership and AI deployment experience, including eBay, Bounty and Catalyser. Leads Canopy’s company direction, product and market development.
Offensive security, digital forensics and application security across government and enterprise. Founder of Blacklight Security; experience includes Commonwealth Bank.
Application security and governance experience across financial services and enterprise, including ASB Bank, Bastion, Helix and Lateral Security.
Security architecture and operations experience, including nearly two decades with the Australian Department of Defence and work in critical infrastructure.
Senior full-stack engineering and technical leadership. Background in cloud migrations, backend development and securing production systems.
Engineering and product delivery experience including Elastic and Booz Allen Hamilton, with work on Kibana data visualisation and enterprise applications.
Walk through one controlled scenario from discovery to policy interpretation, an authorised decision and a tested outcome. Include an unsupported case and the evidence that remains afterwards.
Then review current product readiness, customer validation, deployment economics and the milestones required to build a repeatable business.
Return to the product walkthrough ↑This overview presents Canopy’s product direction and an illustrative operating experience. The film is a reconstructed demonstration using illustrative scenarios, not live screen footage or evidence of a customer deployment. Images and interactive examples are explanatory. Coverage and enforcement depend on supported integrations, permissions and deployment scope. Technical capabilities and security readiness require current validation.